Case file / Project 004
Security Proposal Workspace
A fictional security assessment that brings requirements, controls, evidence, and follow-up actions together.
The purpose
Why I built this
Working in IT has shown me how many security threats organizations face in their day-to-day operations. As AI changes the technology landscape, I want to help build a stronger security posture that can withstand both familiar and emerging risks.
At a cybersecurity summit in Philadelphia, a speaker who led IT at a New York hospital described an incident where default credentials in network settings gave someone a way in. That example stayed with me. A small detail can expose a foundational weakness, even when an organization has invested in other security measures.
The questions
The Questions Behind the Work
This project is helping me connect security frameworks to practical questions:
- Who owns a control?
- What evidence supports it?
- What still needs attention?
The process
From requirements to safeguards
The Security Proposal Workspace grew from my experience working on the technical side of a security proposal. I wanted a way to bring requirements, safeguards, evidence, and follow-up actions together so that gaps are easier to identify and discuss.
The project uses a fictional marketing company to demonstrate that process. For example, it can flag an MFA control that is marked as implemented but has no evidence linked to it.
Proposed architecture
A fictional marketing company
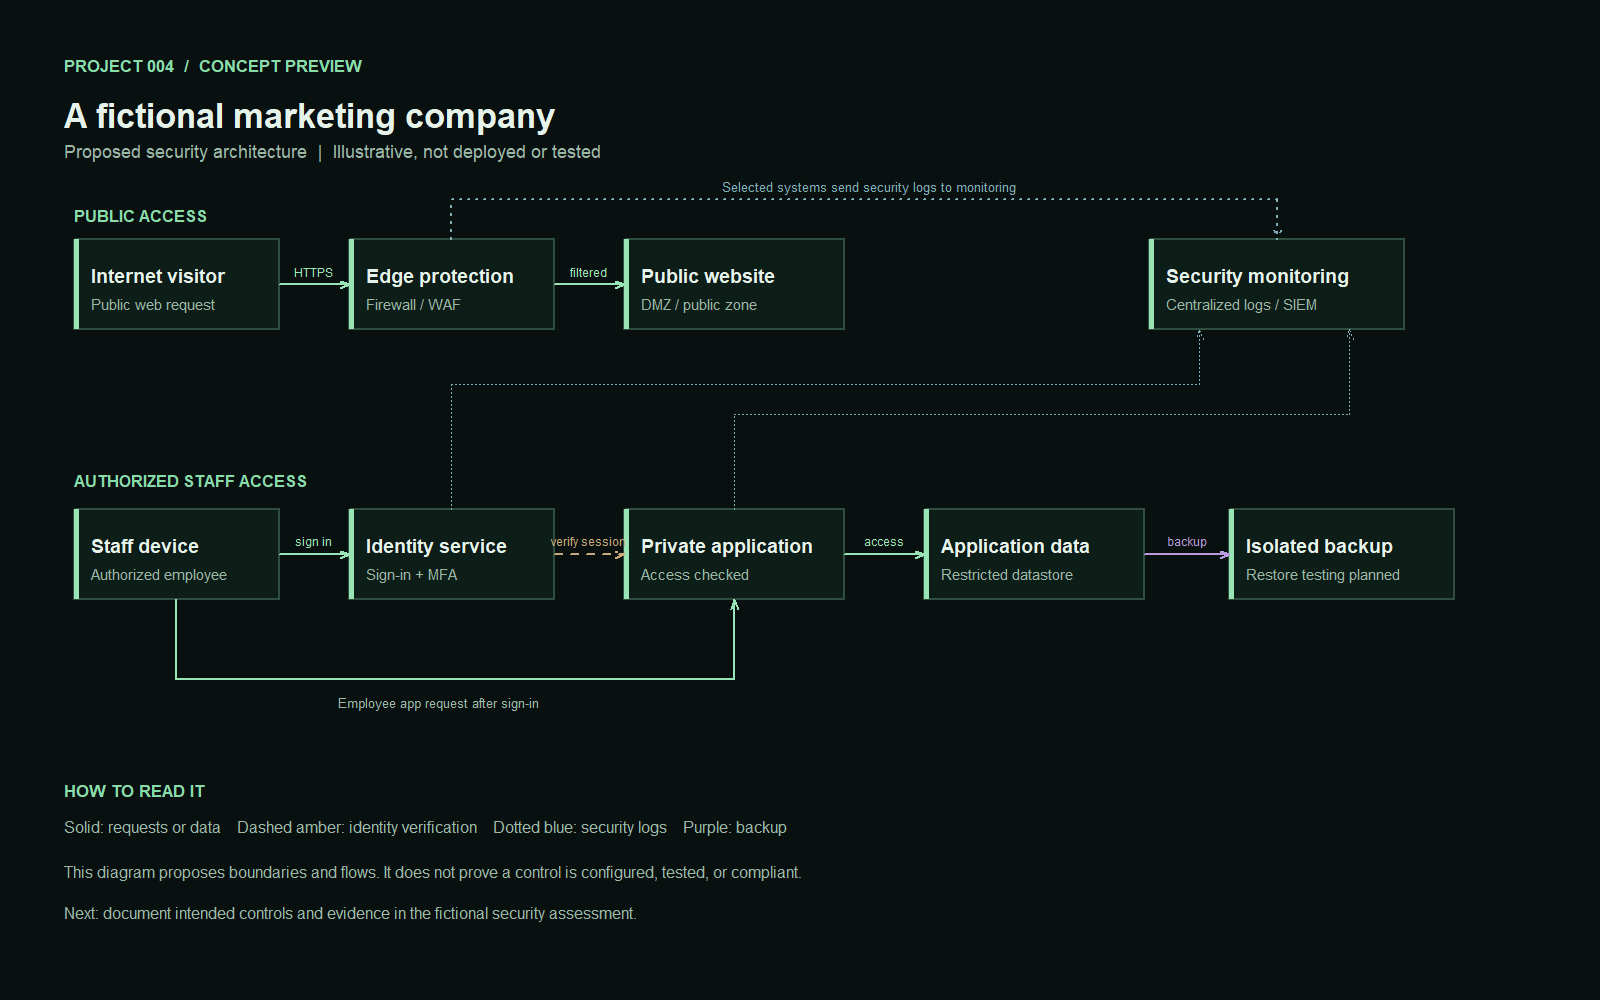
This conceptual design illustrates proposed boundaries and safeguards for the fictional assessment. It is not a deployed or tested system.
View full-size diagram ↗Download editable draw.io file ↓
The diagram is a proposal, not evidence that controls are configured, tested, or compliant.
Reflection
Returning to the questions
Findings and lessons will be added as the hands-on work is completed.